Back to Blog
July 4, 2026
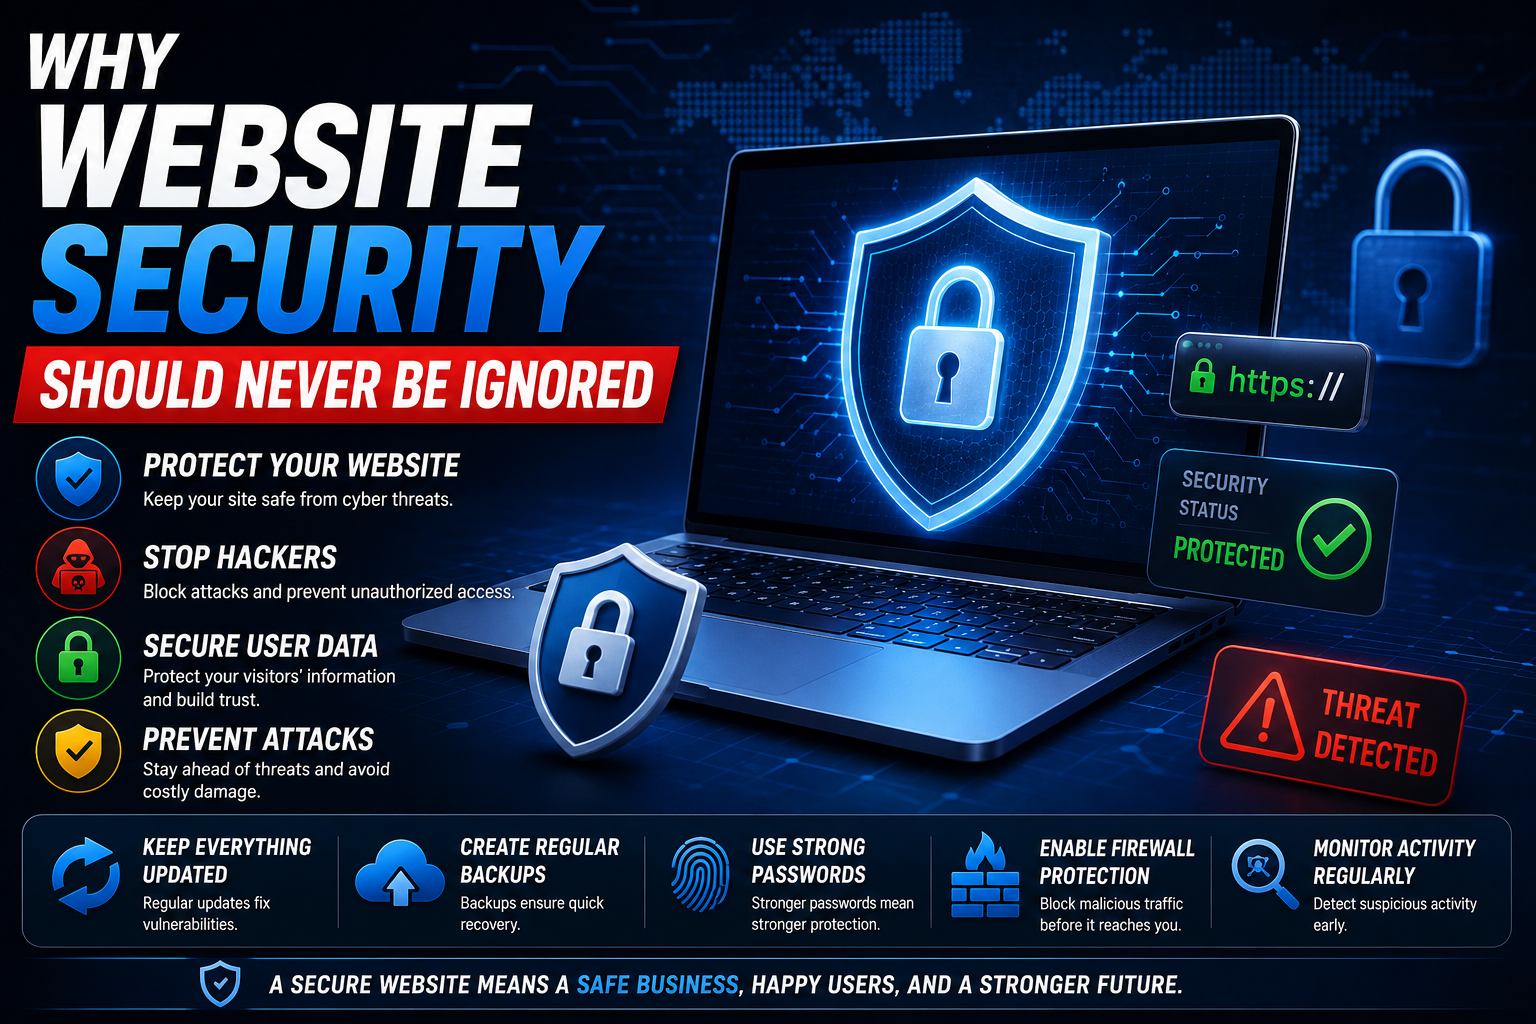
Why Website Security Should Never Be Ignored
Why Website Security Should Never Be Ignored
In today's digital world, every website is a potential target for cybercriminals. Whether you own a personal portfolio, a business website, an online store, or a large web application, security should never be considered an optional feature. Many website owners believe hackers only target large companies, but the reality is that automated attacks scan millions of websites every day looking for vulnerabilities regardless of their size. A single security weakness can expose sensitive information, damage your reputation, interrupt your business, and lead to costly recovery efforts. Building a secure website is no longer just a technical responsibility—it is an essential part of creating a trustworthy online presence.
One of the biggest misconceptions among beginners is that a website becomes secure once it is published. In reality, website security is an ongoing process that requires continuous monitoring, regular updates, and proactive protection. Cyber threats evolve constantly, and attackers are always searching for outdated software, weak passwords, insecure plugins, and poorly written code. Even a small vulnerability can provide hackers with access to sensitive data or complete control of a website. Understanding these risks is the first step toward creating a safer digital environment for both website owners and visitors.
Weak passwords remain one of the most common causes of website compromises. Many administrators continue using simple passwords that are easy to remember but equally easy to guess. Attackers often rely on automated brute-force tools capable of testing thousands of password combinations within minutes. Strong passwords should contain a combination of uppercase letters, lowercase letters, numbers, and special characters while remaining unique for every account. Enabling two-factor authentication adds another important layer of protection by requiring a second verification step before access is granted.
Keeping software updated is equally important. Content management systems, plugins, themes, frameworks, and server software regularly receive security updates that fix newly discovered vulnerabilities. Delaying these updates gives attackers an opportunity to exploit publicly known weaknesses. Regular maintenance ensures that websites remain protected against the latest security threats while improving stability and performance at the same time.
Secure coding practices play a critical role in preventing attacks. Developers should never trust user input without validation. Every form, search field, login page, and file upload feature should carefully verify incoming data before processing it. Techniques such as prepared SQL statements help prevent SQL Injection attacks, while proper output escaping protects against Cross-Site Scripting (XSS). Following secure development standards significantly reduces the risk of common vulnerabilities that attackers frequently exploit.
Encryption is another essential component of website security. HTTPS encrypts communication between browsers and web servers, preventing attackers from intercepting sensitive information such as passwords, payment details, and personal data. Websites without SSL certificates not only expose users to unnecessary risks but may also lose visitor trust and experience lower search engine rankings. Modern browsers clearly identify secure connections, making HTTPS a basic expectation rather than an advanced feature.
Backups are often overlooked until disaster strikes. Hardware failures, accidental deletions, malware infections, or successful cyberattacks can destroy valuable website data within seconds. Maintaining automated backups stored in separate locations ensures that websites can be restored quickly with minimal downtime. Testing backup restoration procedures regularly is just as important as creating the backups themselves because unusable backups provide no real protection during emergencies.
Firewalls and security monitoring tools add another layer of defense by identifying suspicious activity before it becomes a serious problem. Web Application Firewalls filter malicious traffic, block known attack patterns, and reduce the risk of automated exploitation attempts. Continuous monitoring allows administrators to detect unusual login attempts, unexpected file changes, and abnormal traffic spikes that may indicate an ongoing attack. Early detection often prevents small incidents from becoming major security breaches.
Human error continues to be one of the greatest cybersecurity risks. Employees, administrators, and website owners should understand basic security principles, including recognizing phishing emails, avoiding suspicious downloads, and protecting login credentials. Security awareness is just as valuable as technical protection because many successful attacks exploit human mistakes rather than software vulnerabilities.
Website security also directly affects business reputation. Visitors expect websites to protect their personal information and provide a safe browsing experience. A successful cyberattack can result in stolen customer data, financial losses, legal consequences, and lasting damage to brand credibility. Recovering public trust after a security incident is often far more difficult than preventing the attack in the first place. Investing in proper security measures demonstrates professionalism and builds confidence among customers, partners, and clients.
Ultimately, website security should never be viewed as a one-time task or an optional investment. It is a continuous commitment that protects digital assets, preserves customer trust, and ensures long-term business success. By using strong authentication, maintaining regular updates, writing secure code, enabling HTTPS, creating reliable backups, deploying firewalls, and monitoring systems continuously, website owners can significantly reduce their exposure to cyber threats. In an increasingly connected world where cyberattacks occur every minute, prioritizing security is one of the smartest decisions any developer or business owner can make. A secure website is not only safer—it is faster, more reliable, more trustworthy, and better prepared for future growth.